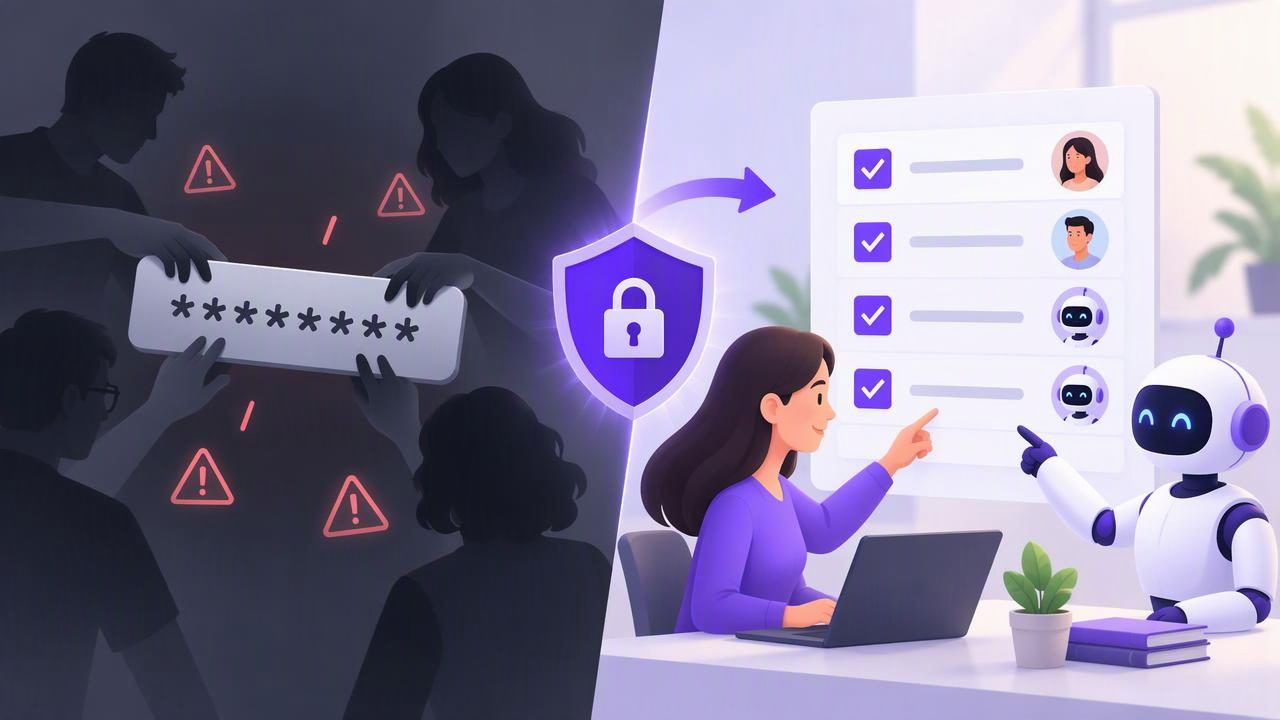
When an AI agent needs to help with your work, it needs a way to understand what should be done. Sharing an account password may seem like the quickest option, but it gives the agent a credential intended for a person—not a clear, limited way to work with tasks. A shared human-agent task list offers a different approach: people and authorized agents refer to the same structured work, while access is managed through a dedicated connection.
Neither approach is automatically safe. A shared task list can still expose information or allow unwanted changes if its access settings are too broad. The useful distinction is that password sharing grants access to an account, while task sharing can provide access to a defined workflow. Understanding what each method permits—and what it does not—is essential before delegating work.
What Is a Shared Human-Agent Task List?
A shared human-agent task list is a common place where a person and an authorized AI agent can read or manage task information. That information might include task names, notes, due dates, priorities, subtasks, and the lists used to organize work. The human can review the plan in their regular task app, while an agent can use an approved integration to perform permitted actions.
The shared list acts as a source of truth for the work itself. Instead of sending an agent a screenshot, pasting a task list into a prompt, or asking it to remember a separate plan, the person and agent can refer to the same current task records. This can make delegation easier to inspect and continue.
However, “shared” does not mean that every person or agent should have unrestricted access. A task system still needs a clear account of who or what can connect, which operations are allowed, and how access can be removed.
Why Shared Passwords Are a Poor Delegation Method
A password often unlocks much more than the particular task an agent is meant to handle. Depending on the service, it may provide access to settings, personal information, billing, or other account functions. The exact exposure varies, but the core problem is the same: the credential does not inherently describe a narrow job such as “read my priorities” or “add a draft task.”
Password sharing also makes accountability and access changes harder. If multiple people or tools use the same login, it may be difficult to tell which action came from whom. Changing the password can disrupt other legitimate users, and leaving the password unchanged can leave old access in place. Some services may also use additional login checks that make sharing credentials unreliable or unsafe.
Most importantly, a password encourages an all-or-nothing decision. Either the agent can sign in as the account holder, or it cannot. That is a poor fit for delegated work, where the intended authority is usually much narrower than the owner’s full account access.
Shared Task List vs. Shared Passwords
| Consideration | Shared password | Shared human-agent task list |
|---|---|---|
| What is shared? | An account credential | Task data through an authorized connection |
| Access shape | May expose account functions beyond the delegated task | Can distinguish reading tasks from making changes, depending on the integration |
| Revoking access | May require changing a shared login and updating other users | A separate token can be revoked without sharing the account password |
| Human oversight | Actions may be difficult to separate from the account owner’s activity | Humans can review the same task records and maintain approval steps |
| Security limitation | Credential access may be broader than necessary | Permissions still have defined limits and should be checked before use |
This comparison is about the access method, not a guarantee that one tool is secure by default. A task list with overly broad permissions can still create risk. Evaluate the actual token scope and available controls, rather than assuming that a task-focused interface automatically limits an agent’s authority.
A Concrete Example: Delegating a Weekly Report
Imagine that you prepare a weekly project report. You want an AI agent to identify tasks that are overdue, group them by project, and draft a short summary. You do not want it to complete tasks, change deadlines, or access the rest of your account.
- Start with the task data. Keep project tasks, due dates, and relevant notes in the task system you already use.
- Choose the narrowest useful access. If the agent only needs to inspect tasks and summarize them, begin with Read Only access where that option is available.
- Give a specific instruction. Ask the agent to report overdue tasks and draft a summary, not to update task status or change due dates.
- Review the result yourself. Check the task records and summary before sharing the report or making decisions based on it.
- Reassess access afterward. Revoke the token if the integration is no longer needed, or keep it only if there is a clear ongoing purpose.
In this example, a shared password would be a poor match because the agent needs task information, not a person’s general account access. A task connection with read-only permission better matches the requested job. If the agent later needs to create draft tasks, Read and Write access may be necessary—but that is a broader permission and should be an intentional choice.
Use Least-Privilege Permissions
Least privilege means giving an agent only the access needed for its current role. It is a practical way to reduce the consequences of mistakes, misunderstandings, or unwanted actions. For task delegation, ask these questions before creating or using an agent connection:
- Does the agent need to read tasks, create them, edit them, or perform several of those actions?
- Can the task be completed with Read Only access?
- Is a separate token available for this agent or workflow?
- Do I know how to revoke that token if the work ends or access is no longer appropriate?
- Am I relying on a filter as though it were a security boundary?
Choose Read Only when the agent only needs to inspect and summarize information. Choose Read and Write only when it needs to make changes, such as adding a task or updating a record, and when the integration explicitly supports that level of access. Permission labels can differ between tools, so read the documentation for the specific connection rather than assuming that every system uses the same rules.
Important Limit: A List Filter Is Not Authorization
A common misunderstanding is to assume that an agent can be restricted to one list simply because a request includes a list identifier. A list_id filter can help select which task records to work with, but a filter is not an authorization boundary. It does not, by itself, prove that the agent is unable to access other data within the scope of its token.
This distinction matters when a task system issues account-scoped tokens. If a token is authorized for an account, do not treat a list filter as though it limits that token to only one list. Follow the documented permission model, and do not build a workflow on the assumption that per-list token permissions exist unless the service explicitly documents them.
For sensitive work, avoid putting information into a connected task account unless the agent’s actual access scope is appropriate for that information. A shared task list is a way to coordinate work; it is not a substitute for understanding the underlying authorization model.
Keep Human Review in the Workflow
Delegation does not require handing over every decision. You can use an agent to find overdue items, suggest priorities, draft task descriptions, or identify missing details while keeping important choices with a person. This is especially useful when a task involves commitments, sensitive information, or deadlines that should not change without approval.
Make the boundary clear in the instruction. For example: “List tasks due this week and suggest a priority order. Do not change due dates, mark tasks complete, or create new tasks.” A specific request gives the agent a manageable job and gives the human a straightforward result to check.
If write access is necessary, consider asking the agent to create clearly described draft tasks rather than making irreversible or consequential changes—provided the task system and workflow support that approach. Review what was added or changed. A human review step is useful, but it does not replace permission controls; both are part of responsible delegation.
When a Shared Task List Makes Sense
A shared human-agent task list can be a good fit when the agent’s job is closely tied to ongoing tasks: summarizing due dates, organizing requests, drafting follow-ups, or adding work after a person approves the plan. It is most useful when people already rely on a task manager and want the agent to work from the current records instead of a copied snapshot.
It may not be the right place for every kind of information. Keep credentials, unnecessary personal details, and sensitive material out of task notes unless there is a clear need and the connected service’s access model is suitable. If the agent needs information from another system, evaluate that connection separately; access to tasks should not be assumed to authorize access elsewhere.
For a native Apple workflow, TaskPort provides shared task management and agent documentation, including an explanation of account-scoped Read Only and Read & Write permissions. Its documentation should be used to understand the supported access model; a list filter should not be treated as a token boundary.
A Simple Decision Rule
Before delegating, describe the job in one sentence. If the sentence is “read these tasks and summarize them,” a read-only task connection is a better conceptual fit than sharing an account password. If the sentence includes making changes, identify exactly which changes are needed and grant only the documented permission that supports them. If you cannot explain what the token allows or how to revoke it, pause before connecting the agent.
The goal is not to give an AI agent the same access as a person. It is to give it enough structured access to perform a clearly defined task, while preserving human oversight and a straightforward way to end access. A shared task list can support that approach, as long as its permissions are understood and its limits are respected.