Claude can help turn a busy inbox, meeting notes, project brief, or daily plan into clear next actions. But when an AI agent connects to a task manager, convenience should not come at the cost of control. The practical answer is revocable MCP access for Claude users: a separate credential that can be limited, reviewed, and disabled without changing the rest of your account.
Model Context Protocol (MCP) gives compatible AI tools a structured way to interact with external services. For task management, that may mean reading task lists, checking due dates, creating follow-up items, or updating a task after you confirm progress. The important question is not just whether Claude can connect. It is what the connection is allowed to do, how long it should remain active, and how easily you can stop it.
This guide explains a practical workflow for using MCP with a task list while keeping humans responsible for priorities, sensitive information, and final decisions.
Why revocable access matters for AI task management
Traditional app connections sometimes use a broad, long-lived account credential. That may be convenient, but it creates unnecessary exposure. If an agent only needs to inspect open tasks for a weekly planning conversation, it should not automatically receive the ability to create, edit, or complete tasks.
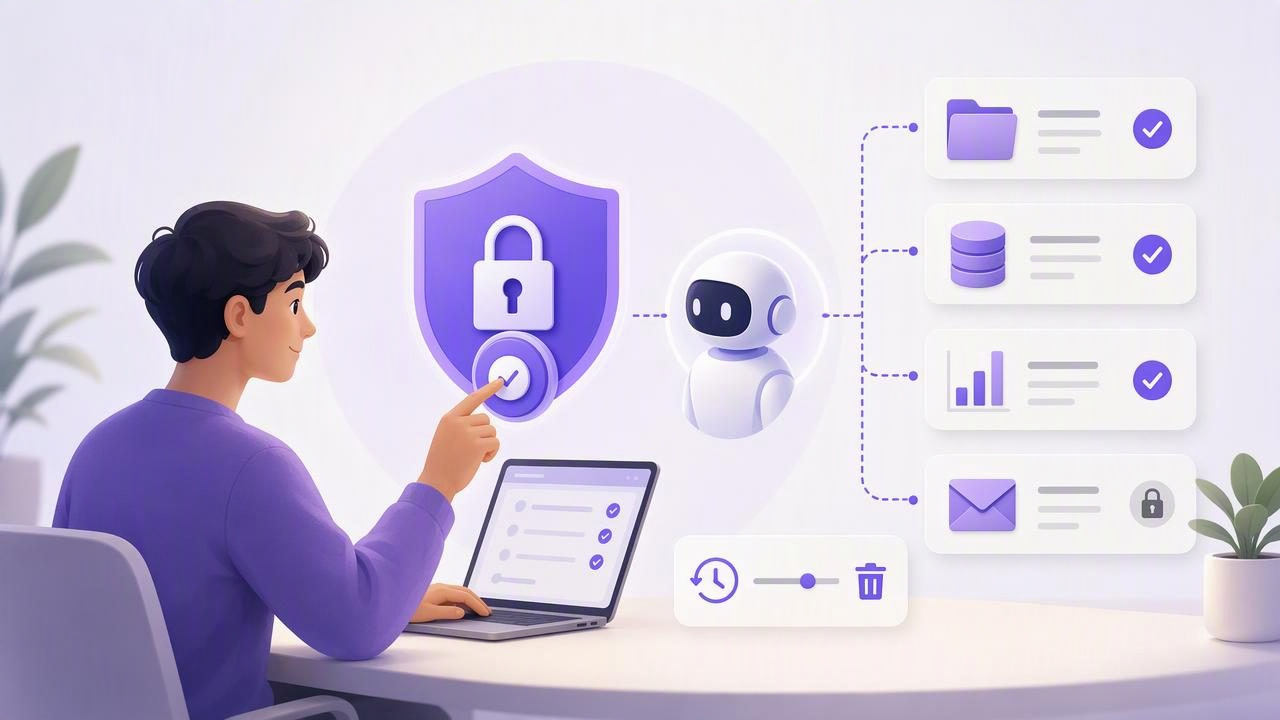
A revocable MCP token is designed around a more controlled approach. You create a distinct token for an agent connection, choose its available permission level, and revoke it when the work is complete or the connection no longer needs access. This makes AI task delegation more manageable in several ways:
- Separation: The agent uses its own access token rather than your primary sign-in details.
- Least privilege: You can choose read-only access when the agent only needs context.
- Containment: A token intended for one workflow does not need to be reused for every agent or experiment.
- Reversibility: You can invalidate the token instead of trying to undo a permanent connection.
- Clearer review: Separate tokens make it easier to understand which agent connection has access.
Revocation is not a substitute for thoughtful permissions. It is the safety net that makes experimentation and delegation less risky. Before granting access, decide what the agent needs to accomplish and choose the narrowest permission level that supports that job.
Understand the two core permission choices
Task-related MCP connections commonly distinguish between Read Only and Read & Write access. The labels are simple, but the operational difference is significant.
| Permission level | Appropriate use cases | What to review |
|---|---|---|
| Read Only | Daily planning, workload analysis, deadline reviews, priority suggestions, and summarizing open work | Whether task names, notes, or dates contain information you are comfortable sharing with the agent |
| Read & Write | Creating tasks from approved notes, adding subtasks, drafting reminders, or updating agreed-upon task details | How the agent will avoid duplicates, unwanted completions, inaccurate dates, and edits to important tasks |
Start with read-only access whenever possible. Claude can still identify overdue tasks, group work by project, flag competing due dates, and propose a realistic daily plan without making any changes. That provides value while keeping your task list fully under human control.
Use Read & Write only when the time saved by direct task creation or updates is worth the added responsibility. Even then, define narrow instructions. For example, tell the agent to create tasks only from a specific meeting transcript you provide and to use a naming convention that makes its additions easy to review.
A concrete Claude workflow: weekly project review
Imagine you manage a product launch with a task list containing research, content, design, approvals, and launch-day work. Every Friday, you want a quick view of what is due next week, which tasks have no due date, and where a priority conflict may exist.
This is a strong read-only use case. Claude needs to inspect task titles, notes, priorities, due dates, and completion status. It does not need permission to reorganize your system.
- Create a dedicated read-only token. Name it clearly, such as “Claude weekly launch review.” Avoid using an old token created for another agent or project.
- Connect it only in the intended compatible Claude environment. Do not paste the token into a chat, a shared document, a screen recording, or a prompt you may reuse elsewhere.
- Set the review scope in your prompt. Ask Claude to focus on active launch work, upcoming due dates, and tasks marked high priority.
- Request recommendations, not actions. Have Claude produce a review that you can inspect before changing priorities or dates yourself.
- Revoke the token when the review cycle ends if this is a one-time connection. For recurring reviews, retain it only while the workflow remains necessary and periodically reassess it.
A useful prompt might look like this:
Review my active launch tasks and return:
1. Tasks due in the next seven days
2. High-priority tasks without due dates
3. Tasks that appear blocked based on their notes or subtasks
4. A suggested Monday-to-Friday plan

Do not make changes. Clearly separate facts from recommendations.
The phrase “clearly separate facts from recommendations” matters. AI-generated suggestions can be useful, but they are not automatically correct. A task labeled “urgent” may already be deprioritized in a conversation the agent cannot see. A date may be a soft target rather than a commitment. Your review supplies the business context.
When write access is justified
Read & Write access can be appropriate when task entry is repetitive and the source material is well defined. For example, after a meeting, you may paste a finalized action-item list into Claude and ask it to create individual tasks with owners, due dates, and notes.
Use explicit boundaries rather than vague instructions such as “organize my tasks.” A safer instruction is:
Create new tasks only for the action items in the meeting notes I provide in this conversation. Do not edit, complete, delete, reprioritize, or move existing tasks. If an owner or due date is unclear, leave it blank and flag it in your response.
This approach reduces accidental changes and makes the resulting task additions easier to audit. It also avoids a common problem with agent workflows: treating assumptions as confirmed facts. If the meeting notes say “Alex will follow up soon,” the agent should not invent a Friday due date.
Know the limitation: filters are not permission boundaries
Some task-manager workflows let you reference a list or use a list_id filter when requesting tasks. This can be helpful for organization and for keeping an agent’s response focused. However, a filter should not be treated as a security boundary unless the service specifically documents it as one.
In particular, account-scoped MCP tokens may allow access according to the token’s overall permission choice. A list filter can narrow a request, but it does not necessarily prevent an authorized read or write token from being used elsewhere in the account. For that reason, do not assume that creating a token “for one list” creates per-list authorization.
This limitation affects how you plan your access:
- Use read-only permissions if the agent only needs analysis, even if you intend to point it at one list.
- Keep highly sensitive notes out of a connected account when possible, or avoid granting an agent account access altogether.
- Create separate tokens for separate agents and workflows so you can revoke one without disrupting another.
- Review and remove tokens that are no longer actively needed.
Least privilege is about what the credential can actually do, not just what you ask the agent to do in a prompt.
Practical security habits for Claude MCP connections
A secure agent workflow is mostly a series of ordinary, repeatable habits. The following checklist applies whether you are planning from an iPhone, reviewing on an iPad, or doing deeper project work on a Mac.
- Use one token per agent connection. Do not share one credential between Claude and another AI agent.
- Name tokens by purpose. Names such as “Claude read-only weekly review” are easier to understand later than “test token.”
- Prefer temporary access. Create access close to the time you need it and revoke it after short-term work.
- Avoid placing secrets in task notes. Passwords, financial identifiers, private keys, and similar material do not belong in a task description available to an agent.
- Inspect write results. After a write-enabled session, check newly created tasks for dates, duplicates, wording, and misplaced priorities.
- Revoke promptly after a concern. If you connect the wrong agent, expose a token, or no longer trust a workflow, revoke first and investigate second.
Also remember that an agent’s access is not the same as its judgment. Claude may summarize a task list well, but it cannot reliably infer hidden dependencies, internal politics, confidential context, or what you meant by an ambiguous note. Keep approval-heavy, sensitive, or irreversible work in a human review loop.
Build a workflow that stays useful over time
The most sustainable AI task management system does not give an agent unlimited autonomy. It uses agents for structured assistance: surfacing gaps, drafting task breakdowns, converting confirmed action items into tasks, and summarizing what needs attention. Humans retain control over priorities, commitments, and exceptions.
Set a simple monthly review reminder for your active MCP tokens. Ask three questions: Does this connection still serve an active workflow? Does it still need write access? Would a new, narrower token be safer than keeping the existing one? These questions take minutes and can prevent forgotten integrations from becoming permanent access.
For users who want a native shared task source across Apple devices and compatible agents, TaskPort’s agent permission documentation explains the available account-token permissions and their use. Whatever tool you choose, treat revocability, permission scope, and regular review as essential parts of responsible Claude task delegation.