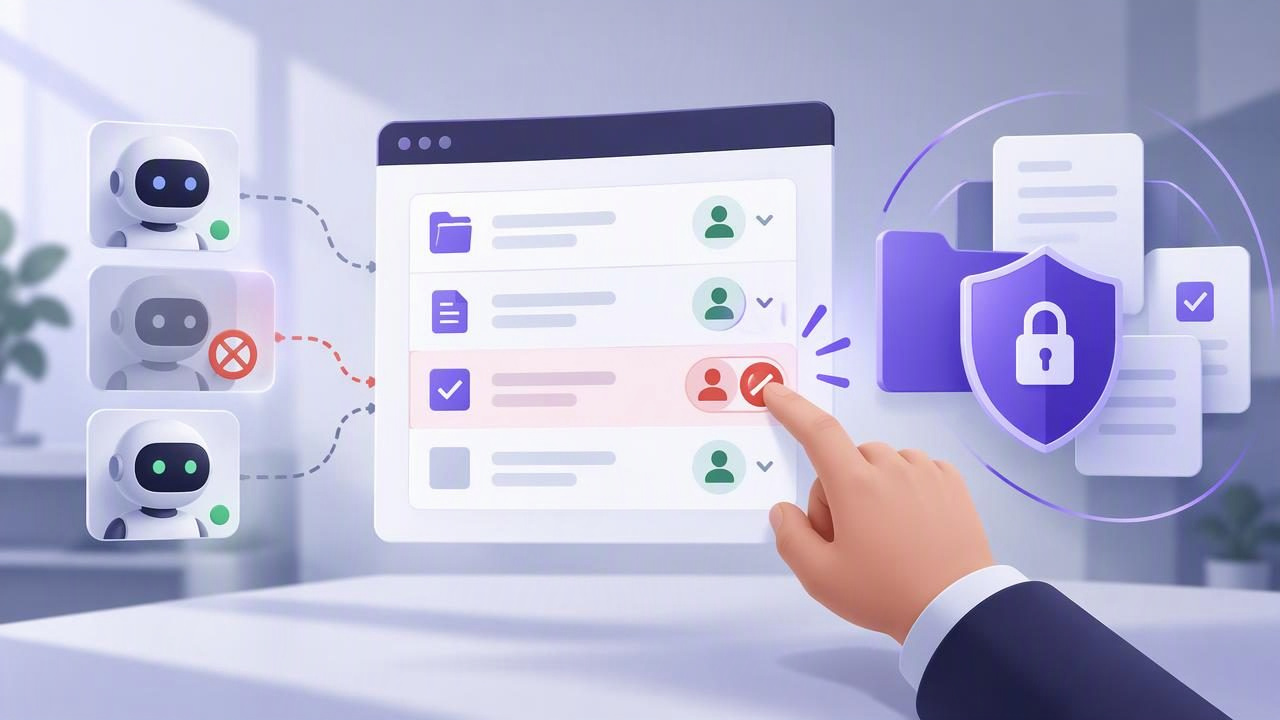
An AI agent can make task delegation faster, but access should never outlast the work it supports. If an agent token is exposed, an experiment ends, or an integration is no longer needed, you need a clear way to cut off its access. That is why an MCP task manager for instant access revocation should be evaluated not only by what an agent can do, but also by how access is granted and withdrawn.
Revocation is a practical security control: it lets you invalidate a credential so it can no longer authorize future requests. It does not undo changes already made or erase information an agent has already received. Understanding that boundary helps you build a safer workflow without treating a token as a substitute for oversight.
What instant access revocation means
In an MCP workflow, an agent uses a credential to access a compatible task manager. Revoking that credential should stop it from being accepted for later requests. “Instant” describes the intended cutoff after the service recognizes the revocation; it does not mean previously returned task data can be recalled or edits can be automatically reversed.
Implementation details matter. A system that checks a token’s validity when processing each request can deny later requests after the token is revoked. If a client or service caches authorization decisions, there may be a delay before the change takes effect. Check the task manager’s documentation for how revocation works rather than assuming that disconnecting an agent, closing its app, or deleting local credentials invalidates the server-side token.
Revocation is also different from changing an agent’s role. A read-only credential limits what the agent is permitted to do while the credential remains valid. Revocation ends that credential’s access altogether. Both controls are useful, but they solve different problems.
Why separate agent tokens matter
A dedicated token gives an agent its own credential rather than requiring you to share your account password. That distinction makes access easier to control: you can issue a credential for a particular integration or workflow and revoke that credential without changing your main account password or disrupting unrelated sign-ins.
Separate credentials also make it easier to respond to uncertainty. If one agent is no longer needed, you can withdraw its token without having to assume every other integration is compromised. Avoid reusing the same token across agents, scripts, or people. When several tools share one credential, it becomes harder to know which one needs access and which one should be cut off.
Token permissions should follow the principle of least privilege: grant only the capabilities required for the task. If an agent only needs to summarize your open tasks, read-only access is a better fit than permission to edit them. If it must create or update tasks, read-and-write access may be necessary, but keep that capability limited to the agent and workflow that need it.
A practical example: ending a planning handoff
Imagine you ask an agent to review your tasks each morning and suggest a realistic plan. It needs to read task names, due dates, and priorities, but you want to approve changes yourself. A read-only token can support that handoff without giving the agent permission to modify the source list. If the trial ends, revoke the token. The agent should no longer be able to make authorized requests with that credential.
Now imagine a different workflow in which an agent creates draft subtasks from a project brief. That may require read-and-write permission. You could use a separate token for that agent, review the resulting tasks, and revoke the credential when the project or experiment is over. If you later resume the workflow, issue a new credential rather than leaving an old, unused one active indefinitely.
In either case, revocation does not remove tasks the agent already created, restore tasks it changed, or delete information it previously read. Review the shared task list after an incident or handoff. Correct or remove unwanted changes yourself, and consider what information may have been exposed beyond the task manager.
Revocation is not the same as per-list access
Check the scope of a token before relying on it. Some task systems issue account-scoped credentials: the token’s permissions apply at the account level rather than being limited to a single list. A list filter may help an agent focus its requests on one project, but a filter is not necessarily an authorization boundary.
For example, adding a list_id filter to a request should not be treated as proof that the token cannot access other lists. A filter can shape which results a request asks for; access control determines what the credential is authorized to retrieve or change. Unless the service explicitly documents list-level authorization, assume that a token’s scope is broader than a chosen list filter and plan accordingly.
This affects how you delegate. If an agent should work only on a sensitive project, do not rely on a request parameter alone to isolate it. Verify the documented permission model, avoid placing unnecessary sensitive information in shared task data, and choose a workflow whose actual authorization scope matches your needs.
A safe access and revocation routine
- Define the job. Write down what the agent needs to read or change before creating access. Avoid granting write capability just in case it might be useful later.
- Use a separate credential. Create a distinct token for each agent or meaningful workflow. Do not paste your account password into an agent configuration.
- Store it carefully. Treat a token like a password. Share it only through the agent’s supported, secure configuration method, and avoid including it in task notes, prompts, screenshots, or source control.
- Review the documented scope. Confirm whether access is read-only or read-and-write and whether it applies to the whole account. Do not infer security boundaries from a list filter or an agent’s intended behavior.
- Set an end point. Decide when the credential should be revoked, such as when a project closes, a trial ends, or an agent is replaced. A token that has no current purpose should not remain active by default.
- Revoke when circumstances change. If a token may have been exposed, or an agent no longer needs access, use the service’s documented revocation control promptly. Do not wait for proof of misuse.
- Check the aftermath. Review task changes and access configuration as appropriate. Revocation blocks future authorized use; it does not reverse previous actions or retrieve data already seen.
What revocation can and cannot protect
| Revocation can help with | Revocation cannot do by itself |
|---|---|
| Preventing a revoked token from authorizing later requests, once the service applies the change | Erasing task details an agent already received or stored |
| Ending access for one dedicated credential without sharing or changing your account password | Undoing tasks created, edited, or deleted before revocation |
| Reducing exposure when an agent or workflow no longer needs access | Guaranteeing per-list isolation when the documented token scope is account-wide |
Think of revocation as stopping the next use of a credential, not as a time machine. It is strongest when paired with restrained permissions, careful token handling, review of agent changes, and a clear understanding of account and list scope.
Questions to ask before connecting an agent
- Can I issue a distinct token rather than sharing account credentials?
- Are the available permissions read-only and read-and-write, and what actions do they cover?
- Are tokens account-scoped, or does the documentation describe a genuine list-level authorization boundary?
- How do I revoke a token, and does the documentation explain when the revocation takes effect?
- What should I review if the agent may have read or changed information before access ended?
These questions apply whether an agent is helping with due dates, priorities, daily planning, or task delegation. Compatibility with an MCP server alone does not answer them; consult the task manager’s official guidance before connecting an agent such as Claude, ChatGPT, Hermes Agent, or OpenClaw.
Build revocation into the workflow
The safest time to plan for revocation is before issuing a token. Match permissions to the task, keep credentials distinct, understand whether access is account-wide, and decide how you will respond when the work ends or a credential is exposed. A well-designed MCP task manager makes those controls understandable, while the human remains responsible for reviewing the consequences of delegated work.
For a concrete example of documented token permissions, TaskPort’s agent permission guidance describes the available access choices and their scope. Use the current documentation for any system you connect, and treat revocation as one part of a broader, least-privilege approach to human and AI agent collaboration.