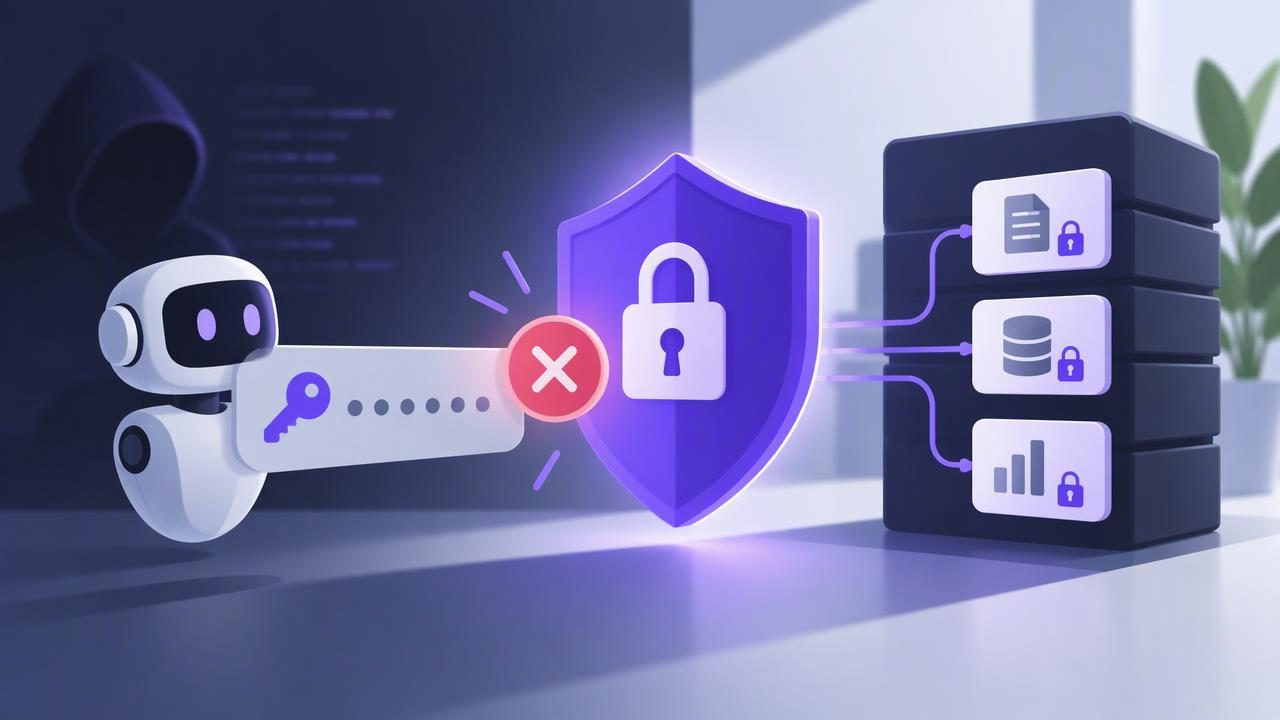
If an AI agent no longer needs access to your tasks—or you think its credential may have been exposed—revoke its token as soon as possible. A token is a credential that lets compatible software access an account under the permissions granted to it. Treat it like a password: share it only with the intended agent, avoid putting it in ordinary messages, and remove access when the job is done.
To revoke an agent token safely, use the service’s documented token-management process, confirm which agent uses the credential, and verify that access has ended. If the agent still needs to work, create a replacement token with only the permissions required. Revocation limits future access, but it does not erase information an agent already retrieved or undo changes it already made.
What revoking an agent token actually does
An MCP token acts as an access credential between a task service and a compatible agent. Depending on its permission level, the agent may be able to read task information, or read and change it. Revoking the token tells the service to stop accepting that credential for future requests.
This is different from deleting the agent, removing a task list, or changing a due date. It also does not necessarily clear copies of task details that were already returned to an agent, recorded in its conversation, or stored in its own logs. Those records are governed by the agent and service involved, so review their retention and data controls separately.
Revocation is useful after a short delegation, a change in team responsibilities, an unexpected agent action, or a possible leak. It is also a good cleanup step when you are testing a new workflow. A token that is no longer needed should not remain active just because nothing appears to be wrong.
When to revoke a token
Act promptly if a token appears in a public repository, screenshot, shared document, or untrusted chat. The same applies if a device or account that could access the credential is lost, an agent behaves unexpectedly, or you cannot identify why a token was created. If you are uncertain whether a credential is exposed, replacing it is generally safer than leaving it active while investigating.
- The delegation is complete: the agent has finished its assigned task and no longer needs access.
- The agent or workflow changes: an old integration should not retain credentials for a new setup.
- The credential may be compromised: revoke first, then investigate where it was used.
- The permission level is too broad: replace write access with read-only access if the work only requires viewing tasks.
- Ownership is unclear: remove tokens that you cannot confidently associate with an authorized agent.
A safe process for revoking and replacing access
- Identify the credential. Check the service’s documented account or token controls and determine which token is associated with the agent or workflow. Do not paste the token into a chat or support request just to identify it.
- Stop or pause the agent if practical. This can prevent repeated failed requests or additional work while you change access. Follow the agent’s documented controls; do not assume that closing a window revokes its credential.
- Revoke the old token through the supported process. Use the documented interface or instructions for the service. Avoid undocumented endpoints or improvised commands, which may not revoke access correctly and could create new security problems.
- Check that the old credential no longer works. Follow the provider’s supported verification method. A rejected request can be a useful signal, but do not test by exposing the token in an unsafe tool or logging it where others can see it.
- Decide whether a replacement is needed. If the agent’s assignment is over, do not create another token. If work continues, issue a new credential and grant only the necessary permission.
- Update the agent’s authorized configuration. Enter a replacement credential only in the integration’s intended secure configuration path. Remove the old value from places you control, such as local notes or configuration files, while remembering that removal cannot guarantee every copy or log has been erased.
- Review recent activity and task changes. If the service or agent provides relevant history, check for unexpected reads or edits. Correct task data if needed, and investigate any incident separately from revocation.
Choose permissions before issuing a replacement
The safest token is not just one that is stored carefully; it is one with no more authority than the job requires. If an agent only needs to summarize open tasks, read-only access may be enough. If it must create or update tasks, read-and-write access may be necessary—but those capabilities also make mistakes more consequential.
| Agent task | Permission to consider | Important limitation |
|---|---|---|
| Summarize tasks or identify overdue items | Read Only | The agent can still receive task information it is authorized to read. |
| Draft proposed task changes for a person to apply | Read Only, if the workflow supports drafting without account edits | Confirm what the agent actually does; do not infer permissions from its prompt. |
| Create or update tasks directly | Read and Write | Review the agent’s instructions and its changes, especially during early use. |
Permission labels describe the access available to the credential, not a guarantee that an agent will behave as intended. Clear task instructions, human review, and secure credential handling remain important even with read-only access.
Do not confuse a list filter with an authorization boundary
A common mistake is to assume that an agent can be safely limited to one list just because its request includes a list identifier or filter. A filter can help select which tasks a workflow asks for, but it is not necessarily a security control. If the underlying token is account-scoped, its authority is determined by the token’s permissions and the service—not by a list filter added to a request.
For that reason, do not promise or rely on per-list token permissions unless the service explicitly documents them. Treat any list selection as a workflow convenience, not as a way to isolate sensitive tasks. If account-wide access would be inappropriate for an agent, do not issue a token until you have confirmed that the documented permission model fits your needs.
Example: ending a task-review delegation
Suppose you ask an AI agent to review your daily plan and flag tasks that may need attention. You provide a read-only token for that work. After the review, the agent no longer needs access. The safe next step is to revoke the token using the task service’s documented controls rather than leave it active for a possible future session.
If you later want the agent to create tasks from meeting notes, first decide whether direct editing is appropriate. If it is, issue a new read-and-write token through the supported process, store it in the integration’s secure configuration, and give the agent a narrow instruction—for example, create tasks with due dates only when a date is explicitly stated. Review the resulting tasks. The new token should replace the old one in the active configuration; it should not be treated as proof that previously retrieved information has disappeared.
Ways to keep an agent token secure
- Use one token per agent or workflow when supported. Separate credentials make it easier to identify and revoke access without disrupting unrelated integrations.
- Keep tokens out of prompts and source code. Use the secure configuration method documented by the agent or service. Never publish a token in a repository or share it in an ordinary message.
- Prefer the least powerful permission. Start with read-only access when it can accomplish the job, and grant write access only when direct edits are required.
- Set a review habit. Periodically check which agent credentials are still needed, especially after experiments or completed projects.
- Revoke rather than merely hide. Removing a credential from a visible settings file does not necessarily invalidate it. Use the service’s revocation process.
Revocation is one part of a safer workflow
Token revocation reduces the chance that an old credential will be used for future access. It cannot reverse completed actions, guarantee deletion of information already seen, or substitute for checking permissions before delegation. For sensitive work, consider what information an agent genuinely needs, whether a person should approve edits, and how you will review the result.
When evaluating an MCP task manager, look for clear documentation about token permissions, revocation, and the scope of each credential. For example, TaskPort’s agent permission documentation explains its Read Only and Read & Write options; confirm the documented account scope and do not treat a list filter as an authorization boundary.
The practical rule is simple: grant only the access required, keep each credential under control, and revoke it when the delegation ends or its safety is in doubt. If ongoing work requires access, issue a fresh token with an appropriate permission level and continue to review what the agent can see or change.