A shared human-agent task list can make AI assistance more practical: you and an authorized agent can work from the same task information instead of relying on scattered prompts or copied updates. But shared access does not automatically mean shared judgment. An agent may interpret a request incorrectly, overlook a dependency, or suggest a deadline that conflicts with your plans.
The safer approach is to decide which actions need human approval before connecting an agent. For many workflows, that means letting the agent read tasks and offer recommendations, while a person reviews and applies changes. If an agent needs permission to make changes itself, treat that as a separate, deliberate decision—not as an assumption built into collaboration.
What human approval means in an AI task workflow
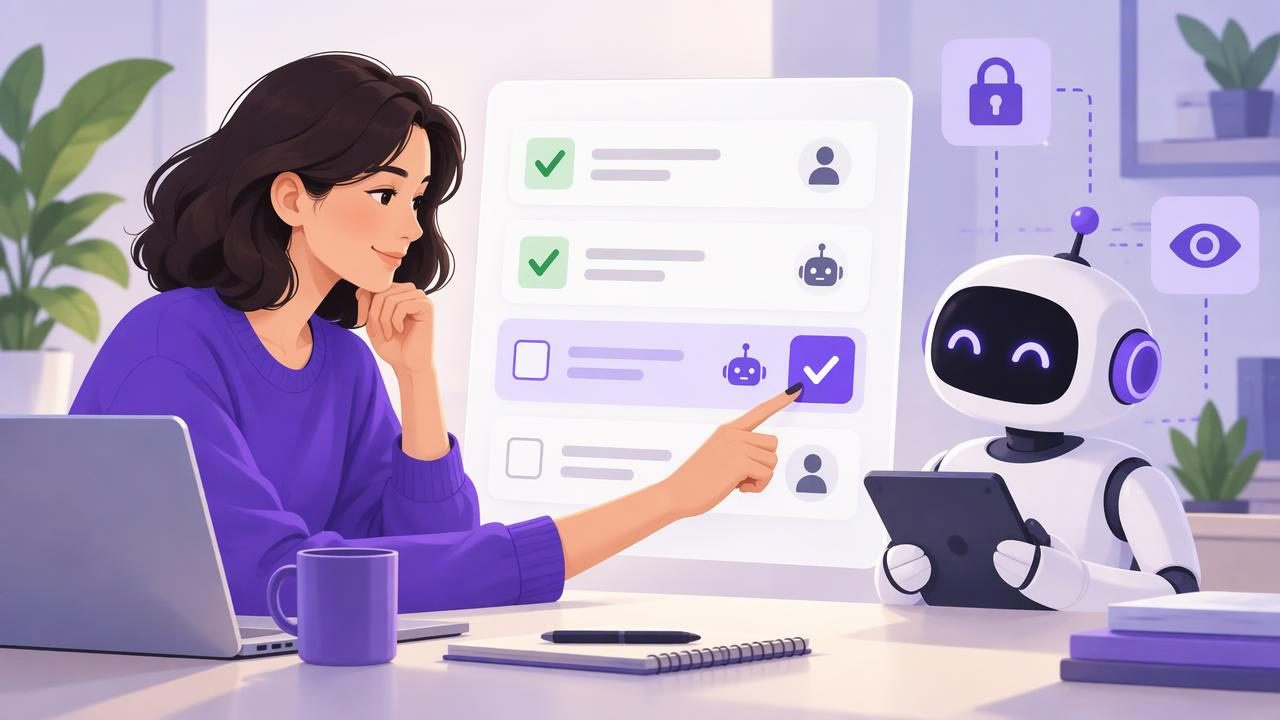
Human approval is a clear checkpoint between an agent’s recommendation and a change that affects your plan. The agent can help interpret information, identify next steps, or draft proposed task details. A person decides whether those suggestions are correct and appropriate before they become active work.
This distinction matters because a task list is more than a collection of ideas. It can include due dates, priorities, subtasks, notes, and commitments. Changing one of those fields may affect what you work on next or what another person expects. A useful workflow makes it obvious which items are confirmed and which still need review.
Approval does not have to mean a formal sign-off process. For an individual, it might be checking an agent’s recommendations during a daily planning session and manually adding the ones that make sense. For a team, it could mean reviewing proposed changes with the task owner before accepting them. The important point is that the agent does not silently turn an uncertain suggestion into a commitment.
Start with the permission level the workflow needs
Before connecting an AI agent to a task manager, ask what it actually needs to do. If it only needs to review tasks and suggest priorities, read-only access may be enough. If it must create or edit tasks, it needs write access—and you should be comfortable with the possible impact of that access.
- Read Only: The agent can use task information as context, but cannot make changes through that access. This supports a review-first workflow in which a human applies approved recommendations.
- Read and Write: The agent can make changes within the scope allowed by its connection. Use this only when direct editing is intentional and the agent’s possible actions are understood.
Permission settings are a boundary, not a substitute for clear instructions or review. Read-only access prevents edits through that token, but it does not guarantee that an agent’s analysis is accurate. Write access makes execution possible, but it does not ensure the agent will pause for approval before every change. If approval must happen before an edit, choose a workflow and permission level that preserve that pause.
A practical approval-first workflow
- Choose the task scope. Decide what information the agent should use, such as your current project tasks or today’s priorities. Be specific in your request, but do not assume a filtered view limits what the token is authorized to access.
- Give the agent the minimum permission needed. Start with Read Only when the job is analysis, planning support, or recommendations. Avoid granting write access simply because it might be convenient later.
- Ask for proposals, not silent changes. Request suggested actions in a reviewable format. For example, ask the agent to identify the task, explain the proposed change, and state any assumptions about priority or timing.
- Review the reasoning and context. Check dependencies, existing due dates, workload, and whether the suggestion matches your actual commitments. A recommendation that looks reasonable in isolation may not fit the rest of your day.
- Apply only approved changes. Make the accepted edits yourself when using read-only access. If you decide to enable write access for a particular workflow, establish a separate human checkpoint and review the task list after the agent acts.
- Reassess access as the work changes. Remove or revoke access when an agent no longer needs it. Create separate credentials for separate agents where supported, so one agent’s access can be managed without treating every connection as the same identity.
This process is intentionally simple. It gives the agent room to help with organization while keeping decisions about commitments, deadlines, and priorities with the person responsible for the work.
Example: approving a change to a project deadline
Imagine that you are preparing a product launch. Your shared task list includes a task called “Review onboarding copy,” with a due date of Thursday, plus a note that the design team must approve the latest screens first. You ask an agent to review the project tasks and identify schedule risks.
With read-only access, the agent can point out that the copy review depends on design approval and suggest checking whether the Thursday deadline is still realistic. It may recommend moving the due date to Friday, but that is a proposal—not an update to the task. You check with the design team, confirm the dependency, and decide whether to change the date. If you approve it, you edit the task and can update its note to explain the reason.
The human checkpoint catches context the agent may not know, such as a firm launch commitment or a conversation that happened outside the task list. It also leaves a clear distinction between the agent’s analysis and your decision. If you had instead given the agent write access, do not assume that asking it to request approval is technically enforced. Use that permission only if you are comfortable with the agent being able to make changes under the granted access.
Keep review manageable with clear task details
Human approval works best when suggestions are easy to evaluate. A task with a specific title, a useful note, an owner or responsible person where relevant, and a meaningful due date gives both the agent and the reviewer better context. Priorities should communicate what matters rather than serving as a substitute for a deadline or dependency.
When asking for recommendations, have the agent separate facts from assumptions. For example, it can identify an existing due date as a fact and label a proposed new date as a suggestion. Ask it to flag missing information instead of filling gaps with confident guesses. These habits make review faster without pretending that the agent knows every commitment behind the plan.
A short daily review can also prevent a backlog of pending decisions. Check proposed changes alongside your existing tasks, accept or reject them, and update the list so the shared view reflects the current plan. If a suggestion is not ready for approval, leave it out of the active schedule until you have enough information.
Understand the limits of tokens and list filters
Token permissions define the access an agent receives, so check whether access is account-scoped and whether it allows reading only or reading and writing. Do not treat a task-list filter, such as a list_id value, as an authorization boundary. A filter may narrow what a particular request returns, but it does not by itself restrict what the token is permitted to access.
That distinction is important when you want an agent to work on one project. A filtered request should not be mistaken for a token that is authorized only for that list. If an agent has account-scoped write access, plan on the basis of that permission scope—not on the basis of a filter in an instruction or request. Where the available permission choices do not match the access boundary you need, do not assume a narrower boundary exists.
Also remember that a token is not a human approval system. A token can limit capabilities, but approval usually depends on the workflow you establish around those capabilities. Separate tokens can help you manage access for different agents, and revoking a token can end that agent’s access. Neither step makes an inaccurate recommendation correct, so continue to review important decisions.
Approval checklist for a shared human-agent task list
- Is the agent’s job analysis, direct editing, or both?
- Can Read Only support the work instead of Read and Write?
- Are proposed dates, priorities, and task changes clearly labeled for review?
- Have you checked the token’s real permission scope rather than relying on a list filter?
- Do you know who will approve a change before it becomes part of the plan?
- Can you revoke access when the workflow or agent no longer needs it?
A shared task list is most useful when everyone can tell what is confirmed, what is suggested, and who is responsible for the next decision. Begin with the narrowest suitable access, keep consequential changes reviewable, and expand an agent’s role only when the workflow genuinely requires it. For an example of how these permission choices are documented, TaskPort’s agent permission guide explains the available access options and their scope.