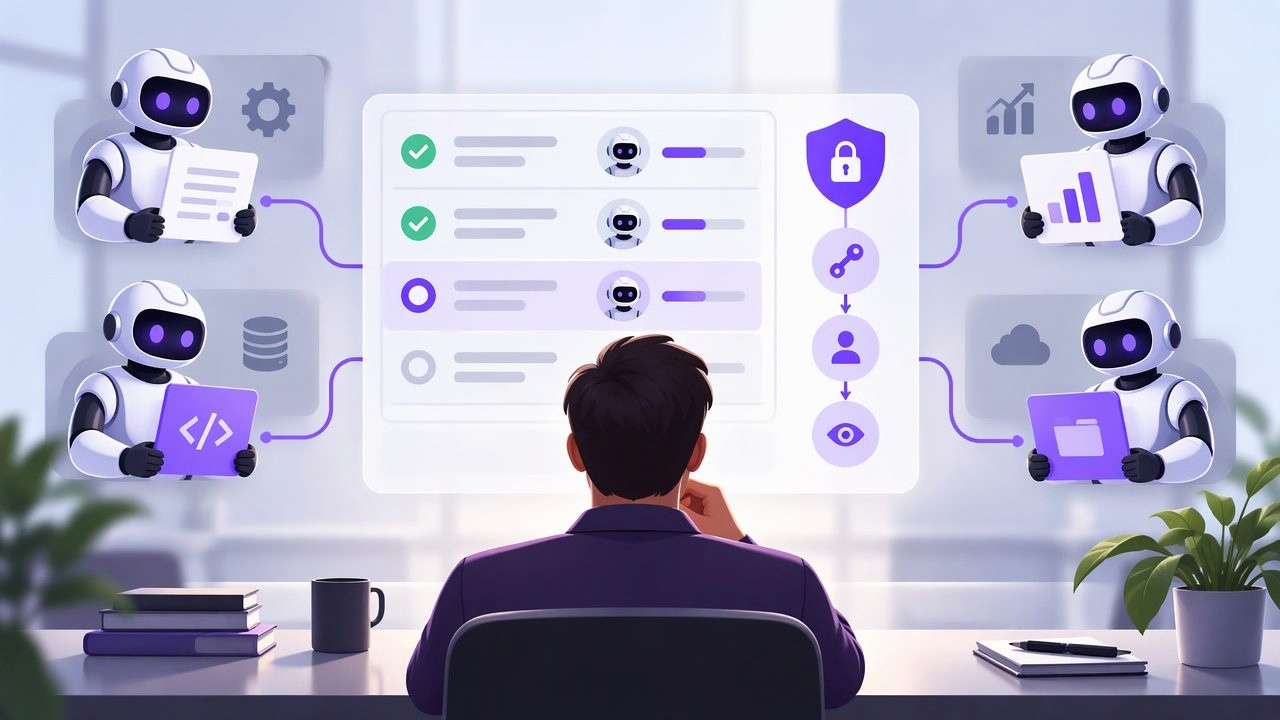
AI agents can help organize a busy day, update task details, and keep work moving. But automation is useful only when you can see what an agent can access and decide what it is allowed to change. An MCP task manager can provide a shared place for people and compatible agents to work with tasks, while permissions and review habits help keep that work controlled.
The practical goal is not to automate everything. It is to give each agent the minimum access needed for a defined job, make its changes easy to inspect, and keep a person responsible for decisions that matter. This guide explains how to build that workflow, with a concrete example and the limitations to understand before connecting an agent.
What makes MCP task automation more controlled?
MCP, or Model Context Protocol, is a way for compatible AI applications to connect with tools and information sources. With an MCP task manager, an agent can interact with task data through the capabilities made available by the task service and its connection. The exact actions depend on the service, the agent, and the configuration; MCP does not mean an agent automatically has access to every possible task operation.
Control comes from several layers working together:
- Permission level: Choose whether an agent can only read task information or can also make changes.
- Token handling: Use separate credentials for separate agents where supported, and revoke a token if it is no longer needed.
- Task design: Write clear task names, notes, due dates, and priorities so the agent has useful context.
- Human review: Inspect consequential changes and keep decisions that need judgment with a person.
- Instructions: Tell the agent what it should do, what it should leave alone, and when it should ask before proceeding.
No one layer replaces the others. A clear prompt does not reduce the access granted by a token, and a read-only connection does not guarantee that an agent’s summary is accurate. Treat permissions as a technical boundary and instructions and review as additional safeguards.
Start with the least access that will work
For a new agent workflow, begin with Read Only access if the agent can complete its first job without changing tasks. This is useful for summarizing open work, finding overdue items, or preparing a proposed daily plan. Review the output before deciding whether write access is actually necessary.
If an agent needs to create or update tasks, use a Read and Write token only when that capability is required. Be precise about the difference between an instruction and an authorization boundary: telling an agent to work only on one project does not technically limit a token to that project.
In particular, a list_id filter can help an agent focus its work, but it is not an authorization boundary. If a token is account-scoped, do not treat a filter or a prompt as a substitute for account-level permission. Review the documented permission model of the task manager before connecting sensitive accounts or data.
Keep credentials private, provide them only through the connection method documented for the relevant service, and do not paste tokens into task notes or ordinary chat messages. If a token is exposed, no longer needed, or assigned to a retired workflow, revoke it using the supported controls. A revoked credential should not be reused as a shortcut; create and configure a replacement through the documented process if access is still needed.
A controlled example: planning a partner webinar
Imagine a small team planning a partner webinar. Its shared list contains tasks such as “Confirm speaker,” “Draft event description,” “Review registration page,” and “Send attendee reminder.” Each task has an owner or useful note, and important work has a due date and priority. The team wants an agent to help with planning without silently making decisions on its behalf.
- Begin with a read-only planning pass. Give a compatible agent read-only access and ask it to summarize tasks due this week, identify items with missing details, and propose a sequence for the next workday. Ask it to cite task names in its response so a person can check the suggestions against the shared list.
- Review the proposal as a person. Confirm whether the speaker deadline is still valid, whether the registration page is actually ready for review, and which task should take priority. The agent can organize available information, but it may not know about a recent conversation or a change that was never entered in the task manager.
- Add write access only for a defined need. If the team decides the agent should create draft follow-up tasks, configure a separate, appropriately permissioned token according to the service’s documentation. Give the agent a narrow instruction, such as proposing tasks for the webinar and marking uncertain details in their notes. Remember that the token’s actual scope—not the wording of the instruction—determines what it can access.
- Inspect changes before relying on them. Check that any new tasks have accurate titles, sensible due dates, and the intended priority. Do not assume that an agent understands an ambiguous date, that a reminder has been sent, or that a task has been completed unless the available task data and your workflow confirm it.
- Reassess access after the work. If the agent no longer needs to make changes, revoke its write-capable token or switch to a lower-access setup where the service supports that choice. Keep only the access required for the next planned job.
This example separates analysis from action. The agent first helps the team understand the task list; a person validates the plan; then any write-enabled automation is used for a specific purpose and checked afterward. It does not rely on a list filter to enforce project-level security.
Make task data easier for agents to handle
Simple to-do lists are often easier to automate than overloaded tasks with vague titles. Use a verb and an outcome in the task name: “Review registration page for broken links” is more actionable than “Registration.” Put background in the notes, and keep separate deliverables as subtasks when that structure is supported by your task manager.
Use due dates when there is a real deadline, not as a guess about when work might happen. Priorities should distinguish genuinely urgent work from tasks that are merely important. If the agent is asked to suggest changes, tell it to flag missing information rather than invent an owner, deadline, or commitment.
Consistency matters across devices, too. A person may add a task on an iPhone, review the day on an iPad, and inspect agent activity from a Mac. Keeping those tasks in one shared source of truth can reduce the need to reconcile separate lists, provided the selected app and agent connection support the intended workflow.
Use separate tokens and a review routine
Where supported, issue separate tokens for distinct agents or workflows rather than sharing one credential everywhere. Separate credentials make it easier to identify which connection to disable when an agent is retired or access needs to change. They do not automatically create per-agent or per-list limits: check whether each token is account-scoped and what its permission choices actually allow.
A short review routine can catch mistakes before they affect the day:
- Compare new or edited tasks with the original request.
- Check due dates, priority, and notes for unsupported assumptions.
- Confirm that proposed work belongs in the intended list.
- Ask the agent to report what it changed, then verify those changes in the task manager.
- Revoke access when an agent or workflow no longer needs it.
For higher-impact actions, make human confirmation an explicit step in the process. An instruction such as “draft the reminder, but do not send it” is useful only if the connected tools and permissions do not let the agent send it through another route. Consider the whole workflow, not just the task manager connection.
Understand the limits of agent automation
An MCP connection does not make an agent infallible. It can misunderstand a request, overlook context, or produce a confident but incorrect summary. Task data can also be incomplete or outdated. Due-date interpretation may vary with wording, locale, or time zone, so use unambiguous dates when the deadline matters.
Permissions have limits as well. Read Only access may still expose information in the account that the agent should not see, so do not connect an account merely because the agent cannot edit it. Read and Write access carries more risk, and a prompt cannot narrow account-level authorization. A list filter may support focused retrieval, but it does not prevent access to other account data unless the service explicitly documents it as a security control.
Finally, an agent can only use the operations made available by its connection and the documentation for that setup. Avoid assuming that a particular action, approval mechanism, audit history, or endpoint exists unless it is documented. When a workflow depends on such a capability, verify it before relying on the automation.
A practical setup checklist
- Define one job for the agent, such as summarizing today’s tasks or drafting follow-up items.
- Start with read-only access when it is sufficient.
- Use a separate token for each agent or workflow when supported.
- Confirm whether permissions apply to an entire account; never treat a list filter as a security boundary.
- Write clear tasks with meaningful notes, due dates, and priorities.
- Require a person to review important changes and decisions.
- Revoke credentials that are no longer needed, and consult official documentation for setup and permissions.
Controlled automation is a balance: give agents enough access to reduce repetitive work, but keep the boundaries and review steps visible. For teams using TaskPort, the agent permission documentation explains its Read Only and Read and Write choices; check those details alongside your own workflow before connecting an agent.