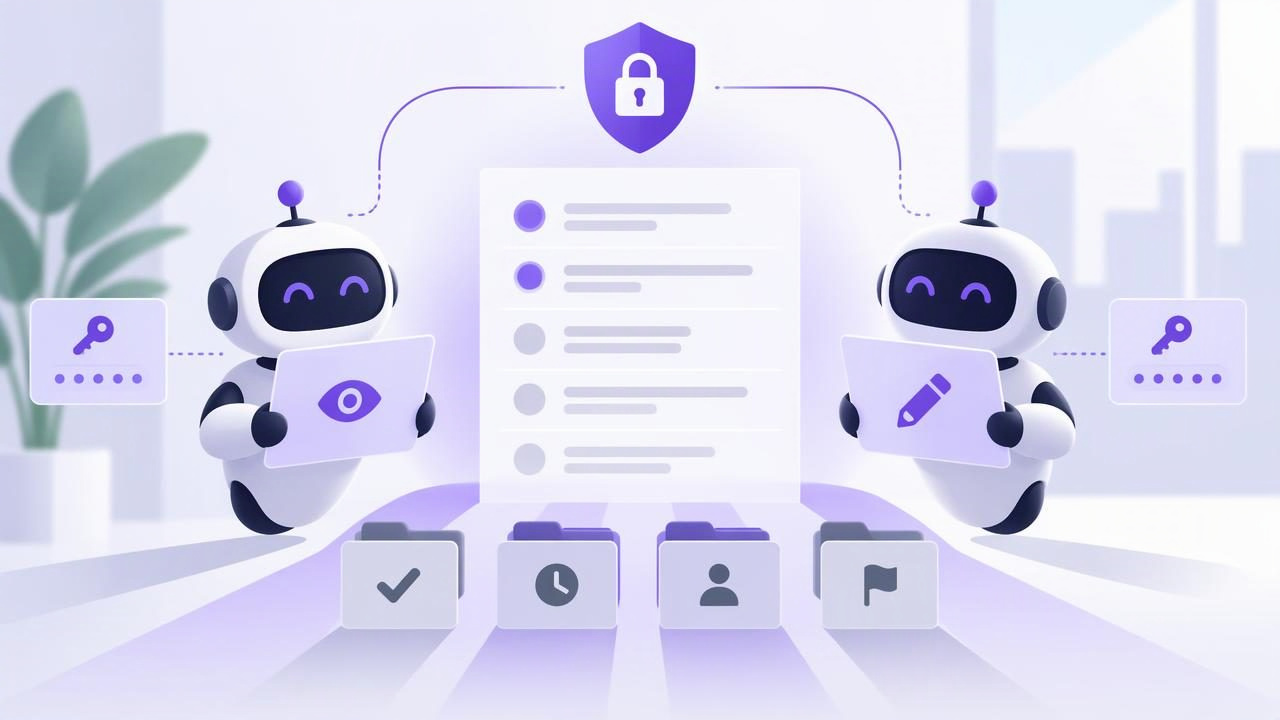
When an AI agent can work with your tasks, it becomes easier to delegate—but also easier to lose track of what the agent can see or change. A useful agent permission system for better task visibility makes access understandable before work begins: people know which agent is connected, what it can do, and where human review is needed.
This is not just a security question. Clear permissions can also prevent accidental edits, make delegated work easier to audit, and help people distinguish an agent’s contribution from their own. The goal is to give each agent enough access for a defined job, while keeping decisions and accountability visible.
What task visibility means when agents are involved
In a shared task manager, visibility has several parts. You need to know which tasks an agent can read, whether it can make changes, and how its work fits into the larger plan. You also need a reliable way to stop access when an agent or workflow is no longer needed.
Permissions and organization solve different problems. Lists, due dates, priorities, notes, and subtasks help people understand work. Permissions determine what an authorized agent is allowed to do. A well-organized task list does not automatically restrict access, and a permission setting does not make vague tasks clear.
Start with the smallest useful permission
Before connecting an agent, write down the specific task you want it to perform. Then decide whether that task requires reading information, making changes, or both. Begin with the least access that still allows the workflow to work, rather than granting broad access for convenience.
- Read Only: Appropriate when an agent needs to inspect tasks, summarize priorities, or help you reason about a plan without editing it.
- Read and Write: Appropriate when an agent needs to create or update tasks as part of a defined delegation workflow.
- No connection: Appropriate when the task contains information the agent does not need, or when the workflow is not ready for agent access.
Read and Write access should not mean that every proposed change is automatically accepted. A person can still review the task list, check an agent’s changes, and decide what to keep. Permission describes technical capability; it does not replace an approval process.
Match permissions to the work
A simple access plan makes it easier for teammates to understand why an agent has a connection. Use a table like this as a planning aid, then confirm the actual options offered by the task manager and compatible agent you use.
| Agent activity | Starting access | Human checkpoint |
|---|---|---|
| Summarize today’s due tasks | Read Only | Check the summary before changing priorities |
| Suggest a project breakdown | Read Only | Review the proposed subtasks before adding them |
| Create follow-up tasks from an approved plan | Read and Write, if required | Review new tasks, due dates, and notes |
| Change a high-impact deadline | Keep the decision with a person unless the workflow explicitly permits the change | Confirm the deadline with the responsible person |
The table is a decision aid, not a guarantee that every integration supports each action or a particular approval feature. Capabilities can vary between task managers, agents, and MCP connections, so check the relevant documentation before relying on a workflow.
Use separate tokens to make access easier to manage
If multiple agents or workflows connect to the same task account, separate tokens can make access clearer. A token assigned to one agent is easier to identify and revoke than a credential shared among several tools. Use a descriptive internal label for each token, such as “weekly planning assistant” or “project follow-up agent,” so its purpose is recognizable during a review.
Keep tokens private. Do not paste them into task notes, shared documents, public code, or messages where people who do not need access can find them. If a token is exposed, no longer needed, or associated with a retired agent, revoke it through the supported controls and review whether another connection needs attention.
Understand the scope before you connect. In some systems, a token’s permission applies at the account level. A list filter may help an agent focus on relevant tasks, but a filter is not an authorization boundary. If the token can access the account, do not assume that asking the agent to use one list prevents it from accessing other account data. Confirm the documented permission model rather than inferring security from a query or filter.
Concrete example: delegating a launch checklist
Imagine you are coordinating a small product launch. Your task list includes copy review, a support FAQ, a release note, and a launch-day reminder. You want an agent to identify missing steps and suggest a sensible order, but you do not want it to move the launch date or rewrite approved copy without review.
- Connect for review. Start with Read Only access if the agent only needs to inspect the existing checklist and point out gaps.
- Make the request specific. Ask it to identify missing launch tasks, explain dependencies, and suggest dates for your consideration. Tell it not to treat suggestions as approved changes.
- Review the response. Compare its suggestions with the real constraints, owners, and commitments. Add or revise tasks yourself if that is all the workflow requires.
- Expand access only if needed. If you later want the agent to add approved follow-up tasks, check whether the integration supports that action and whether Read and Write access is required. Use a human review step for the new tasks and their due dates.
- Close the loop. When the work is complete, decide whether the agent still needs access. Revoke a token that is no longer required.
This example separates analysis from execution. The agent can help make work more visible by surfacing gaps, while the person responsible for the launch retains control over commitments and consequential edits.
Make tasks readable to both people and agents
Permissions cannot compensate for unclear task descriptions. Give delegated tasks a concrete action, enough context, and a useful deadline when one is known. For example, “Prepare launch materials” is hard to assess; “Draft the release note for review before Thursday’s launch meeting” communicates an action, an output, and a checkpoint.
Use priorities consistently rather than marking everything urgent. Add notes when an agent needs context that is not obvious from the task title, and use subtasks to make larger work easier to review. A daily planning routine can help: scan what is due, identify the few tasks that matter most, and decide which items are suitable for delegation.
Agree on how an agent should report uncertainty. It should be able to flag missing information or conflicting dates rather than silently guessing. For example, if a task has no confirmed owner or the proposed date conflicts with a stated milestone, make that ambiguity visible and ask for human direction.
Review access as the workflow changes
Permissions are not a one-time setup. A Read and Write token that made sense for a short project may be unnecessary after the project ends. New agents, changed responsibilities, and different task data can all affect whether existing access is still appropriate.
Periodically check which agents are connected, what each token is intended for, and whether its permission still matches that purpose. When an agent’s role changes, reassess its access instead of assuming the original choice remains suitable. If the available permission choices are account-wide, account for that scope when deciding whether the connection is appropriate.
A practical checklist for safer task visibility
- Define the agent’s job before connecting it.
- Choose Read Only when the job does not require changes.
- Use Read and Write only when the workflow needs edits.
- Keep tokens separate, private, labeled, and revocable.
- Check whether permissions apply to the whole account.
- Never treat a list filter as a security control unless the documentation explicitly says it restricts authorization.
- Make tasks clear with action-oriented titles, useful notes, due dates, and consistent priorities.
- Review agent suggestions and consequential edits with the responsible person.
- Revoke access when a token or workflow is no longer needed.
Better visibility comes from clear boundaries
A useful agent permission system combines understandable task organization with deliberate access choices. Start with the agent’s job, grant only the access that job requires, and make the human review point explicit. Separate tokens can make connections easier to manage, while clear due dates, priorities, notes, and subtasks help everyone understand the work itself.
For a practical reference, TaskPort’s agent permission documentation explains its account-scoped token choices, including Read Only and Read and Write, and why a list filter should not be treated as an authorization boundary.