An AI agent can help organize tasks, summarize a busy list, or update work after you give it instructions. But sharing a to-do list with an agent also raises an important question: what should it be allowed to see and change? The answer depends on the job you delegate—and on whether the access method lets you limit permissions clearly.
An AI agent to-do list with permissions is a shared task system where an authorized agent can access tasks through defined access choices, rather than through a person’s password. A careful setup can make human and AI agent collaboration more useful while reducing unnecessary access. It does not remove the need to review changes, protect credentials, or understand the scope of a token.
What task permissions do for an AI agent
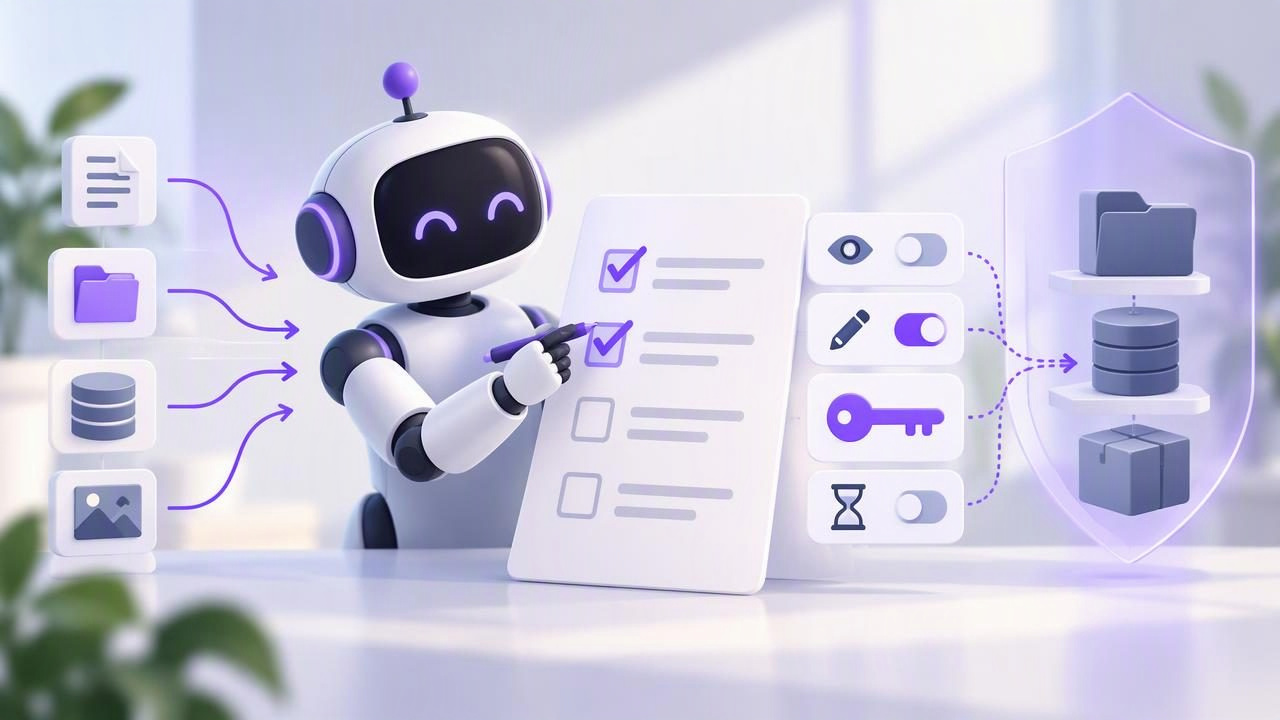
Permissions describe what an agent can do with the task information it receives. A read-only connection lets an agent view available task data without making changes. A read-and-write connection lets it both view and modify task data within the scope of that account connection.
Those choices matter because common requests can require different levels of access. Asking an agent to summarize overdue tasks is a viewing job. Asking it to add a due date, change a priority, or create a task is a modifying job. If the agent only needs to report information, read-only access is generally the more appropriate starting point.
Permissions are not a guarantee that an agent will interpret instructions correctly. They define what it can access through the connection; they do not decide whether a proposed change is wise, prevent every mistake, or replace your review.
Match access to the task you are delegating
Before connecting an agent, describe the work in plain language and identify whether it needs to read, write, or both. That small check can prevent granting broader access than the job calls for.
| Delegated job | Likely access needed | Human check |
|---|---|---|
| Summarize tasks due today | Read Only | Confirm the summary reflects the right tasks and dates. |
| Identify tasks without due dates | Read Only | Decide which tasks should receive a date. |
| Add an approved due date or priority | Read and Write | Check the task and values changed. |
| Create tasks from meeting notes | Read and Write | Review titles, details, owners, and dates before relying on them. |
When a task needs only a recommendation, ask the agent to suggest a change rather than apply it. You can then make the update yourself. When direct updates are useful, state which changes are allowed and what should be left untouched. A permission setting controls technical access; clear instructions define the intended task.
A concrete example: planning a busy Monday
Imagine you have several work and personal tasks due Monday. You want an agent to spot conflicts and help you make a realistic plan, but you do not want it rearranging your list without approval.
- Start with a read-only request. Ask the agent to review tasks due Monday, group them by priority, and point out any missing information. It can provide a proposed schedule or identify tasks that may need attention without changing the underlying list.
- Review the suggestions. Check that the agent has understood the due dates and priorities. You might decide that a task marked urgent can wait, or that a personal appointment must take precedence. Your judgment remains part of the planning process.
- Choose any approved updates. If you want the agent to add an agreed due date or create a task from a specific note, use a connection with write access only when that action is necessary. Give a narrow instruction, such as: “Add a task to send the revised brief by 2 p.m. Monday. Do not change other tasks.”
- Verify the result. Check the shared list after the agent acts. Confirm the title, due date, priority, and any other changed details. If the agent’s actions are not right, correct them and adjust the instructions before delegating a similar job.
This workflow separates analysis from action. It is useful when you want AI support for daily planning but still want to decide which tasks become commitments.
Understand token scope before connecting
Some task systems use tokens to authorize an agent. A token acts like a credential for the permissions assigned to it, so it should be handled carefully. Check whether the token is tied to an account, what access choices are available, and how to revoke it if it is no longer needed. Do not paste tokens into public messages, shared documents, or prompts that do not need them.
Also distinguish a filter from an authorization boundary. A list_id filter can help request or display tasks from a particular list, but it is not the same as a permission restriction. If a token is account-scoped, adding a list filter does not turn it into a token that is authorized only for that list. Do not rely on filters to protect other account data.
That distinction matters when you share tasks across workstreams. If you need an agent to focus on one project, tell it which list to use and verify its actions—but do not assume that focus instruction changes the token’s underlying access. Read the integration’s documentation to understand the actual permission boundary.
Use separate, revocable access for agents
Where the system supports it, use a separate token for each agent or integration instead of reusing one credential everywhere. Separate credentials make it easier to identify which connection you intend to disable if you stop using an agent, change your workflow, or suspect a token was exposed. Use only the access level needed for that connection.
Revocation is an important part of access management. If an agent is no longer authorized, revoke its token through the documented controls. Removing an instruction from a chat is not the same as revoking a credential. Likewise, deleting an app or changing a task list may not disable an existing token. Follow the service’s documented process and confirm the connection should no longer have access.
Token security also depends on where credentials are stored and how they are passed to compatible software. Follow the agent and task manager’s official setup guidance; avoid inventing connection steps or sending credentials to unverified tools. If a token may have been exposed, revoke it and create a replacement using the documented process.
Keep human review in the workflow
Read-and-write access can save effort when an agent is authorized to carry out routine task updates. It also means an incorrect interpretation could result in a changed task list. The right safeguards depend on the impact of the change. A spelling correction may be easy to spot; moving a deadline or changing a priority could affect your day.
- Specify the allowed action. Name the task or the type of update, and say what must not change.
- Prefer suggestions for uncertain decisions. Ask the agent to propose a date or priority when context is incomplete.
- Check important edits. Review changes that affect commitments, timing, or other people.
- Keep task details understandable. Clear titles, notes, due dates, and priorities make the shared source of truth easier for people and agents to interpret.
- Reassess access. When a workflow changes, ask whether the agent still needs write access.
These habits are especially useful when several agents are involved. A clear division of work—for example, one agent summarizes while another applies specifically approved updates—can reduce confusion. But separate roles only help if each connection’s actual permissions and instructions are understood.
Check compatibility and limitations
Not every AI agent can connect to every task manager. The agent and task system must support a compatible integration, and setup details can vary. Claude, ChatGPT, Hermes Agent, and OpenClaw are examples of agents named in TaskPort’s integration context; compatibility depends on the supported connection and the agent’s own configuration. Always check current documentation rather than assuming a particular feature or connection method is available.
Permission choices also have limits. Read-only access does not mean the agent can see only the specific information you mention in a prompt if its authorized connection can read broader account data. Read-and-write access should not be described as per-list access unless the service explicitly documents that boundary. A list filter, agent instruction, or separate chat is not a substitute for an authorization control.
For implementation details, review the TaskPort agent permission documentation, including the documented account-scoped Read Only and Read & Write choices. The key is to understand the connection’s real scope before sharing access.
Build a safer human-agent task workflow
A useful AI agent to-do list with permissions is not simply a list connected to an assistant. It is a shared workflow with an intentional access level, clear delegation, protected credentials, and human review where the decision matters. Begin with read-only access for analysis, add write access only when the agent needs to make changes, and use separate revocable credentials when available.
Most importantly, treat permission settings as boundaries for access—not as a substitute for careful planning. When you understand what an agent can see and change, you can delegate specific task work with more confidence while keeping control of your priorities, due dates, and daily plan.